Pennington County Confirms Ransomware Attack on July 4th
Pennington County, South Dakota, confirmed that a cybersecurity incident on July 4th was a ransomware attack. County officials took servers offline to contain the threat, and while departments are operational, some public-facing services remain limited as recovery efforts continue.
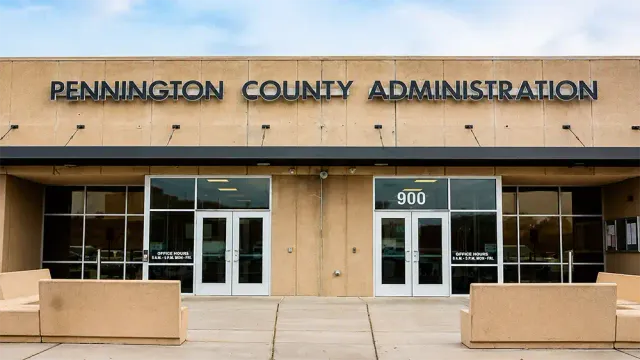
 Rapid City, SD, September 24, 2026 — Pennington County, South Dakota, has confirmed that a cybersecurity incident that occurred on July 4th was a ransomware attack. The county government disclosed the nature of the breach following an investigation into the event.
In response to the detected threat, county officials took immediate action by taking servers offline. This measure was implemented to contain the ransomware and prevent further unauthorized access or damage to the county’s digital infrastructure.
While internal county departments have resumed operational activities, the attack has had an impact on the availability of some public-facing services. These services remain limited as recovery efforts are actively underway. The county has not provided specific details regarding which services are affected or the estimated timeline for full restoration.
The contractor involved in the cybersecurity incident was not identified in the provided information. Similarly, the extent of the data compromised, the specific ransomware variant used, and the potential financial impact or ransom demands were not disclosed. The status of permits, inspection outcomes, code violations, or fine amounts related to this incident were also not provided.
Recovery operations are ongoing, and county officials are working to restore full functionality to all systems and services. Further updates are expected as the investigation and restoration process progresses.
Story summarized from the original created by KOTA Staff on www.kotatv.com, see more information here.
Media gallery